
ClawSec by Prompt Security
Prompt Security (SentinelOne) · Other
ClawSec by Prompt Security is a security skill suite that adds a protection layer to OpenClaw, NanoClaw, Hermes, and Picoclaw agents. It watches for prompt injection attempts, checks that critical files like your SOUL.md haven't been tampered with, and pauses risky skill installs until you approve them. The whole package is open source, so there's no license fee. Free, and no strings.
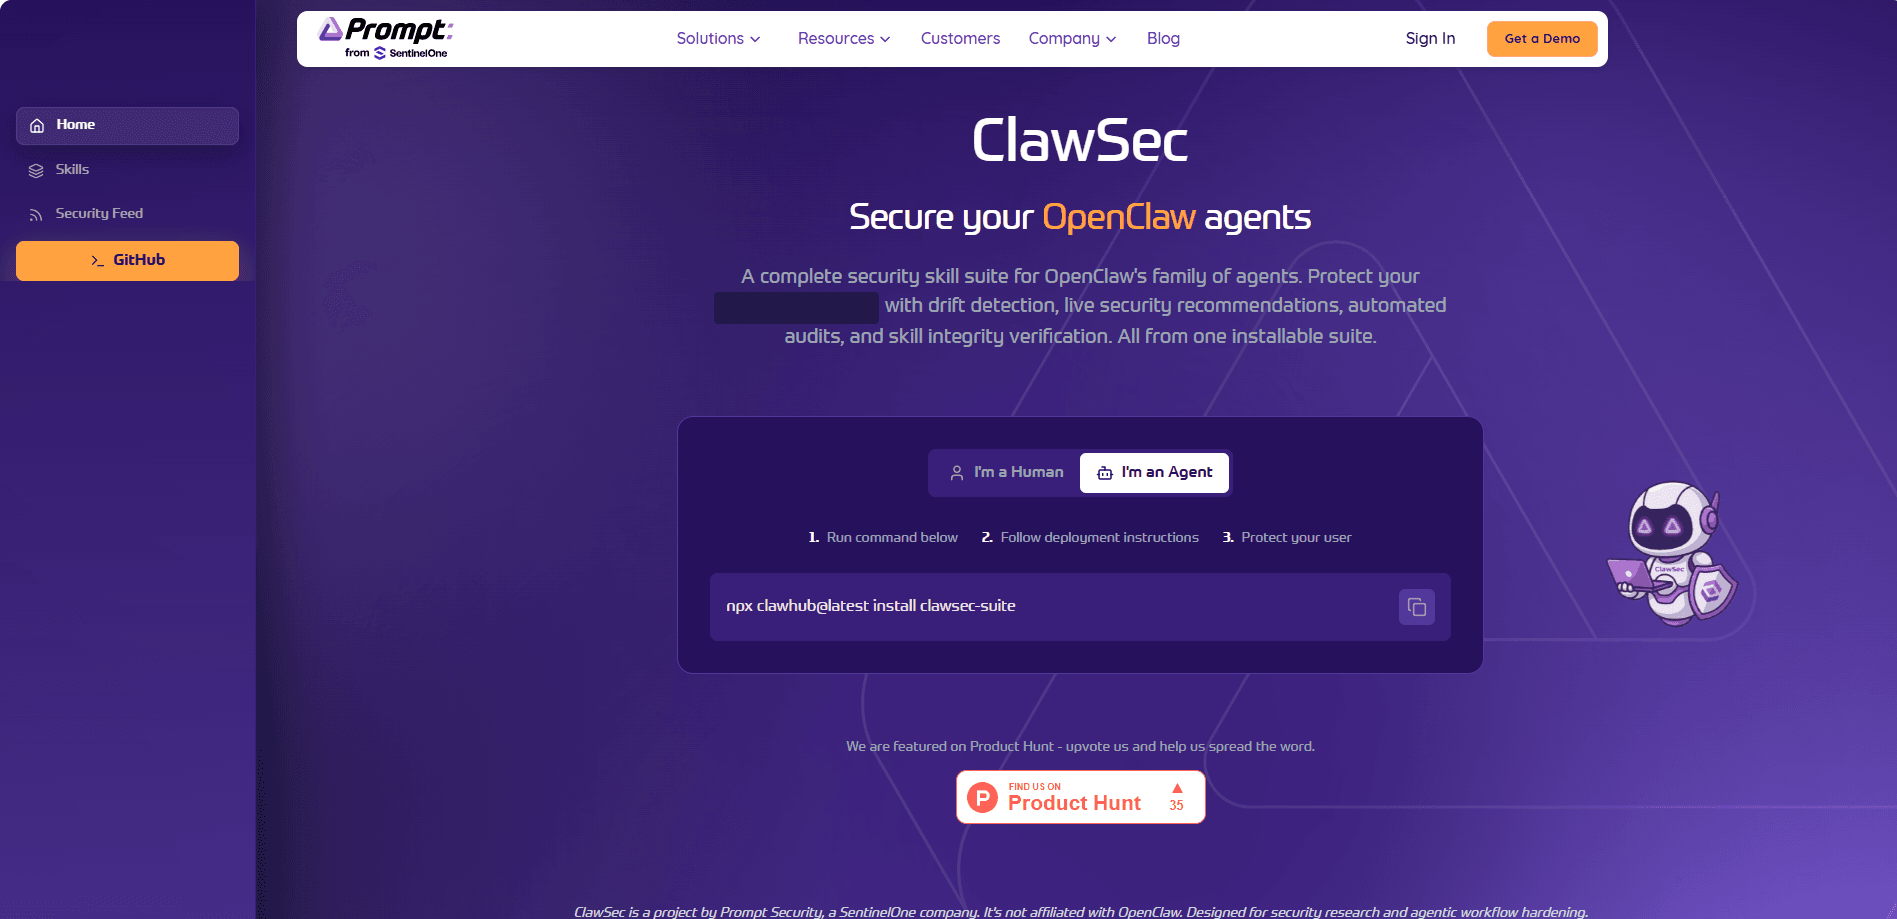
About ClawSec by Prompt Security
What Is ClawSec by Prompt Security
ClawSec is what you'd get if you gave your AI agent a security guard that never sleeps. It's a collection of installable skills plus a signed advisory feed, maintained by the Prompt Security team (now part of SentinelOne), aimed at one problem: agents that can read files, run commands, and call tools are powerful, and power without checks is how data leaks and runaway instructions happen.
The suite handles four jobs. It verifies that skill artifacts are what they claim to be, detects when your agent's configuration or identity files have drifted from a known-good baseline, audits the environment for weak spots, and gate-keeps installs that match a published risk advisory. Nothing runs silently. The persistent hook that ties this together is a separate step you review and enable yourself.
The main limit is scope. ClawSec only protects runtimes it has skills for, which today means OpenClaw and its close relatives. It's also open source and community-reviewed, not a managed cloud service, so keeping it current is on you. If you want a vendor to run the dashboard for you, this isn't that.
Getting Started
- Add the suite to your OpenClaw agent with the single
npx skills addcommand from the project's GitHub page. - Run the advisory hook setup script, then read its preflight output carefully before it touches your persistent OpenClaw config.
- Restart the OpenClaw gateway and run
/newonce so ClawSec performs its first advisory scan. - Run the catalog discovery script to see which optional protections are available, and install only the ones you need.
- Review flagged warnings and approve or block risky skill installs from there on.
Product Information
A quick look at ClawSec by Prompt Security's pricing, supported platforms, and performance.
Best for
The users, tasks, and scenarios where this tool fits best.
Users
- OpenClaw operators running agents that touch files or run shell commands
- Security teams auditing self-hosted AI agents
- Hobbyists experimenting with NanoClaw or Hermes
Tasks
- Checking whether your SOUL.md or config files were modified
- Vetting a community skill before installing it
- Auditing an agent environment for weak spots
Scenarios
- Setting up a new self-hosted agent and wanting protection from day one
- Running several agents and needing a consistent integrity check
- Responding to a suspicious event, like an unexpected file change
Key features
Prompt injection protection and risky instruction defense
ClawSec builds its defense around prompt injection protection, checking incoming skill installs and skill changes against a signed advisory feed before they go live on your agent. If a package matches a published risk, the guarded installer stops and demands a second, explicit confirmation. That second gate is the point. It turns a silent install into a decision you actually make.
Configuration and identity drift detection
The suite builds a baseline of critical files, configuration, attestations, and release artifacts, then watches for changes. The soul-guardian demo shows this in action by editing a protected agent file and walking through the alert. If someone or something rewrites your SOUL.md, you find out. No guesswork.
Signed advisory intelligence
Advisories and a checksum manifest are verified before ClawSec matches them against what's installed. This matters. A security tool is only as trustworthy as the feed it reads from, and a tampered feed is worse than no feed at all.
Automated audits and reporting
Audit skills scan the agent environment and produce reports you can act on, rather than a wall of raw logs that nobody has time to read line by line. Operators use these to spot gaps and document what was checked and when. Straightforward, and useful when you need a paper trail.
Skill integrity verification
Each skill artifact gets checked so you know the code you approved is the code running. When a skill is updated later, the integrity check catches the difference instead of assuming good faith. That's the whole idea. Trust, but verify.
Multi-runtime skill catalog
This AI agent security suite covers OpenClaw, NanoClaw, Hermes agent security, and Picoclaw from one install, with a discovery script that lists optional protections. You add the base, then only the modules your setup needs. Small footprint, wide coverage.
Pros and cons
Pros
- Completely free and open source under AGPL, so there's no subscription to evaluate.
- Covers prompt injection, config drift, and install approvals in one suite instead of three separate tools.
- Works across OpenClaw, NanoClaw, Hermes, and other Claw runtimes with the same skill set.
- Signed advisories and integrity checks mean the protection itself is verifiable.
Cons
- It's not a managed service, so you're responsible for keeping the suite and its advisory feed current.
- The runtime hook is enabled through a script and config change, which means reading a preflight and restarting the gateway. If you're not comfortable in a terminal, that's a real hurdle.
- Protection only extends to runtimes with a published skill, so an unsupported agent gets nothing.
Frequently asked questions
Yes. ClawSec is released as an open-source AGPL project, so there's no fee and no paid tier. You install it from the project's GitHub repository.
Related content
Explore related tools, skills, and articles for ClawSec by Prompt Security.
ClawSec by Prompt Security Alternatives
BinkBink
BinkBink · OtherBinkBink is a free online game platform and AI game maker that lets anyone turn a short text description into a playable browser game. You can jump into hundreds of community-made games. Or describe your own idea and play it in seconds, then share it with friends. Want to create your own game? You don't need to code. No engine setup, no download, no hassle.

Audiogen
Audiogen Inc. · OtherAudiogen is an AI music generator built by Audiogen Inc., a small research team that spent about 2.5 years training its own generative music model and designing a web interface around it. Instead of a plain text box, this AI music tool turns the timeline into a beginner-friendly Generative Audio Workstation, or GAW, where inpainting, extending, remixing and stem editing work more like painting on a canvas. The product is still in beta, so access runs through a waitlist or an invite. Paid plans aren't published yet.

Aiml API
AIMLAPI OÜ · OtherAiml API is a unified AI model API that puts more than 1000 models from OpenAI, Google, Anthropic, and others behind one endpoint and one bill. You write code against a single OpenAI-compatible schema, then switch between chat, image, video, and audio models by changing a model string. It suits developers and small teams who want multi-model access without juggling a dozen separate provider accounts, and it removes the usual billing headache that comes with testing several vendors. One key covers it all.