
Proof & Trust
Proof&Trust · Other
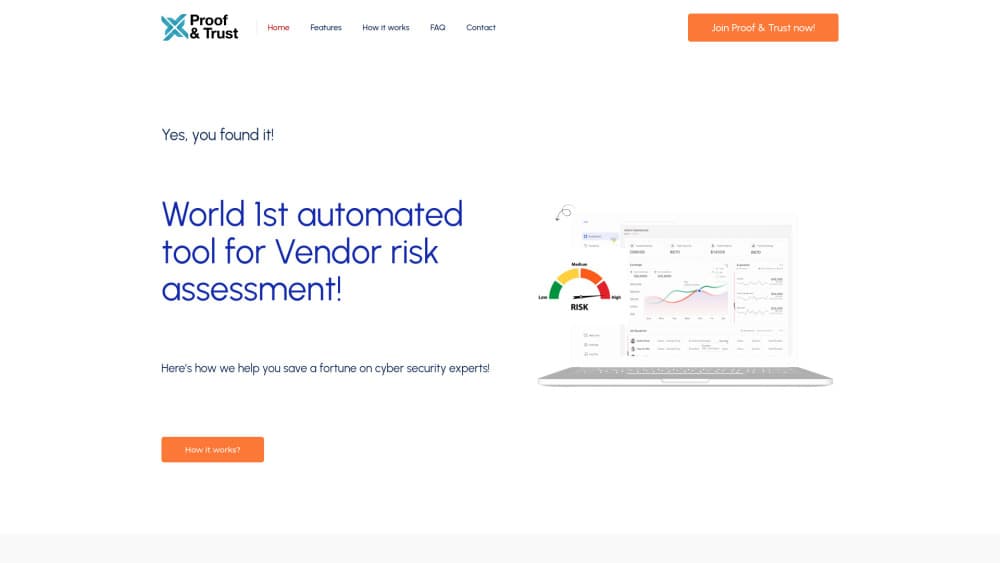
Proof&Trust scores and tiers NIS2 supply chain vendors from their own evidence, replacing static questionnaires with audit ready risk reports in under 30 minutes.
About Proof & Trust
What Is Proof&Trust
Proof&Trust is a web platform for NIS2 supply chain risk. It runs a vendor risk assessment on every supplier, sorts the results into risk tiers, and keeps a running evidence trail that mirrors what auditors ask for. Think of it as third party risk management built for one regulation: instead of a vendor security questionnaire, you start scoring the certificates, reports, and attestations vendors already hold.
The product exists because of the EU's NIS2 Directive, which has applied since 17 October 2024. Article 21(2)(d) makes the security of direct suppliers the responsibility of the buying company, so a spreadsheet of expired questionnaire answers no longer counts as due diligence. Proof&Trust reads the underlying documents, confirms their validity, and maps each control to the exact clause it satisfies. That is evidence grade scoring, as opposed to a survey that simply records what a vendor claims.
The limits matter as much as the pitch. Proof&Trust is a compliance and risk tool, not a firewall or a scanner, and it aims at EU regulated teams in banking, energy, healthcare, telecom, and the public sector. Deployment is EU hosted by default, and bigger scopes go through sales rather than a self serve checkout. Annual plans start at €1,999.
Getting Started
- Book a demo or ask for the 30 minute sample, which returns a scored portfolio with no integration and no credit card.
- Upload a batch of supplier evidence, such as ISO 27001 certificates, SOC 2 reports, SBOMs, pen test attestations, and written policies. Connect contracts and vendor records if you have them.
- Let the engine parse, validate, and score each artifact, then roll the scores into a single vendor risk index.
- Invite suppliers through a link so they can answer the built in questionnaires at the right risk level and upload fresh proof.
- Review the tiered portfolio in the console, then export the audit pack for your reviewers.
Product Information
A quick look at Proof & Trust's pricing, supported platforms, and performance.
Best for
The users, tasks, and scenarios where this tool fits best.
Users
- Compliance and GRC teams at EU essential entities
- CISOs and security leads in banking, energy, healthcare, telecom, or the public sector
- Small supplier teams formalising a first programme
Tasks
- Replacing a spreadsheet of vendor questionnaires
- Tiering a backlog of suppliers
- Preparing for an NIS2 audit
- Drafting an Article 23 incident notification
Scenarios
- A regulator requests supplier evidence
- A supplier discloses a breach or a new CVE lands
- A board review on cybersecurity risk
Key features
Evidence Grade Vendor Scoring
Every artifact a supplier sends, whether an ISO certificate, a SOC 2 report, or a pen test attestation, gets parsed, checked against its issuer, and scored on completeness, recency, scope, and control coverage. Those scores then roll into one vendor risk index. The value is simple: you are scoring documents you can defend, not answers someone typed into a form.
Automated Vendor Tiering
NIS2 vendor tiering here runs on three signals, and vendors classify into Critical, High, Standard, and Limited tiers. The first is how essential the supplier is to your service, the second is how concentrated your exposure is, and the third is how strong the evidence is. The model is deterministic and explainable, so any tier change links back to the evidence event that caused it.
Continuous Re Tiering
Tiers are not a one off exercise. They recalculate when fresh evidence arrives or a signal weakens, and event driven checks pick up CVEs, sanctions, and breach disclosures. A supplier that looked safe last quarter can escalate the moment its exposure crosses the threshold.
NIS2 Article 21(2) Mapping
The platform covers all ten measures in Article 21(2), from risk analysis and supply chain security through to MFA and secure communications. Each score ties to a specific clause, and that mapping is usually the first thing an auditor reaches for.
Article 23 Incident Drafting
When you log a qualifying incident, Proof&Trust pre fills the Article 23 notifications. That covers the 24 hour early warning, the 72 hour incident notification, and the one month final report, with timestamped facts, affected vendors, and impact estimates ready for your CSIRT to review.
Auditor Evidence Export
The audit workspace exports a portable pack as PDF and machine readable JSON. It mirrors what reviewers see in the live console, so you hand over one file instead of assembling screenshots and spreadsheets.
Flexible Deployment
Proof&Trust ships as a multi tenant EU hosted service, a single tenant environment, or a private deployment in your own VPC on AWS, Azure, GCP, or OVH. Every option shares the same evidence model and scoring engine, and data stays in the EU by default.
Pros and cons
Pros
- It scores hard evidence rather than questionnaire answers, which is the part auditors and regulators actually inspect.
- Tiers recalculate on their own, so a new CVE or a disclosed breach does not have to wait for the next review cycle.
- Pricing starts at €1,999 a year for 20 assessments, which is low for a supply chain programme.
- Every score cites its source artifact and the NIS2 article it meets, so the portfolio holds up in a review.
- It is EU hosted by default, with single tenant and private VPC options for data residency needs.
Cons
- It is built around NIS2 and EU firms, so teams outside the EU or outside the Directive's scope get little value from it.
- There is no free tier and no self serve signup, so you start with a demo or a paid plan rather than a trial.
- The API export ships on the Enterprise plan only, which means smaller plans move data by CSV.
- It tracks supplier paperwork, not your own systems, so it does not replace a vulnerability scanner or a pen test.
Frequently asked questions
It is NIS2 compliance software that scores and tiers the vendors in your supply chain, turning their certificates, reports, and attestations into a single risk index and an audit ready portfolio.
Related content
Explore related tools, skills, and articles for Proof & Trust.
Proof & Trust Alternatives

Odyssey 3
Odyssey · OtherOdyssey-3 is Odyssey's foundation world model. It simulates physics in real time, turns a prompt into an interactive environment, and adapts to robots, cars and games.

JarvisCore
Prescott Data · Coding · Productivity · OtherJarvisCore is an open source Python runtime where AI agents work as equal peers on an agent mesh, claim tasks from a shared ledger, and reach external services through a zero-trust broker.
Clef
Cloudflare · Business · OtherClef is Cloudflare's open-source decision model for Workers AI. It returns calibrated probabilities for typed questions, not generated text, so agents can classify, route, and act fast.