
Bevel
Bevel · Coding
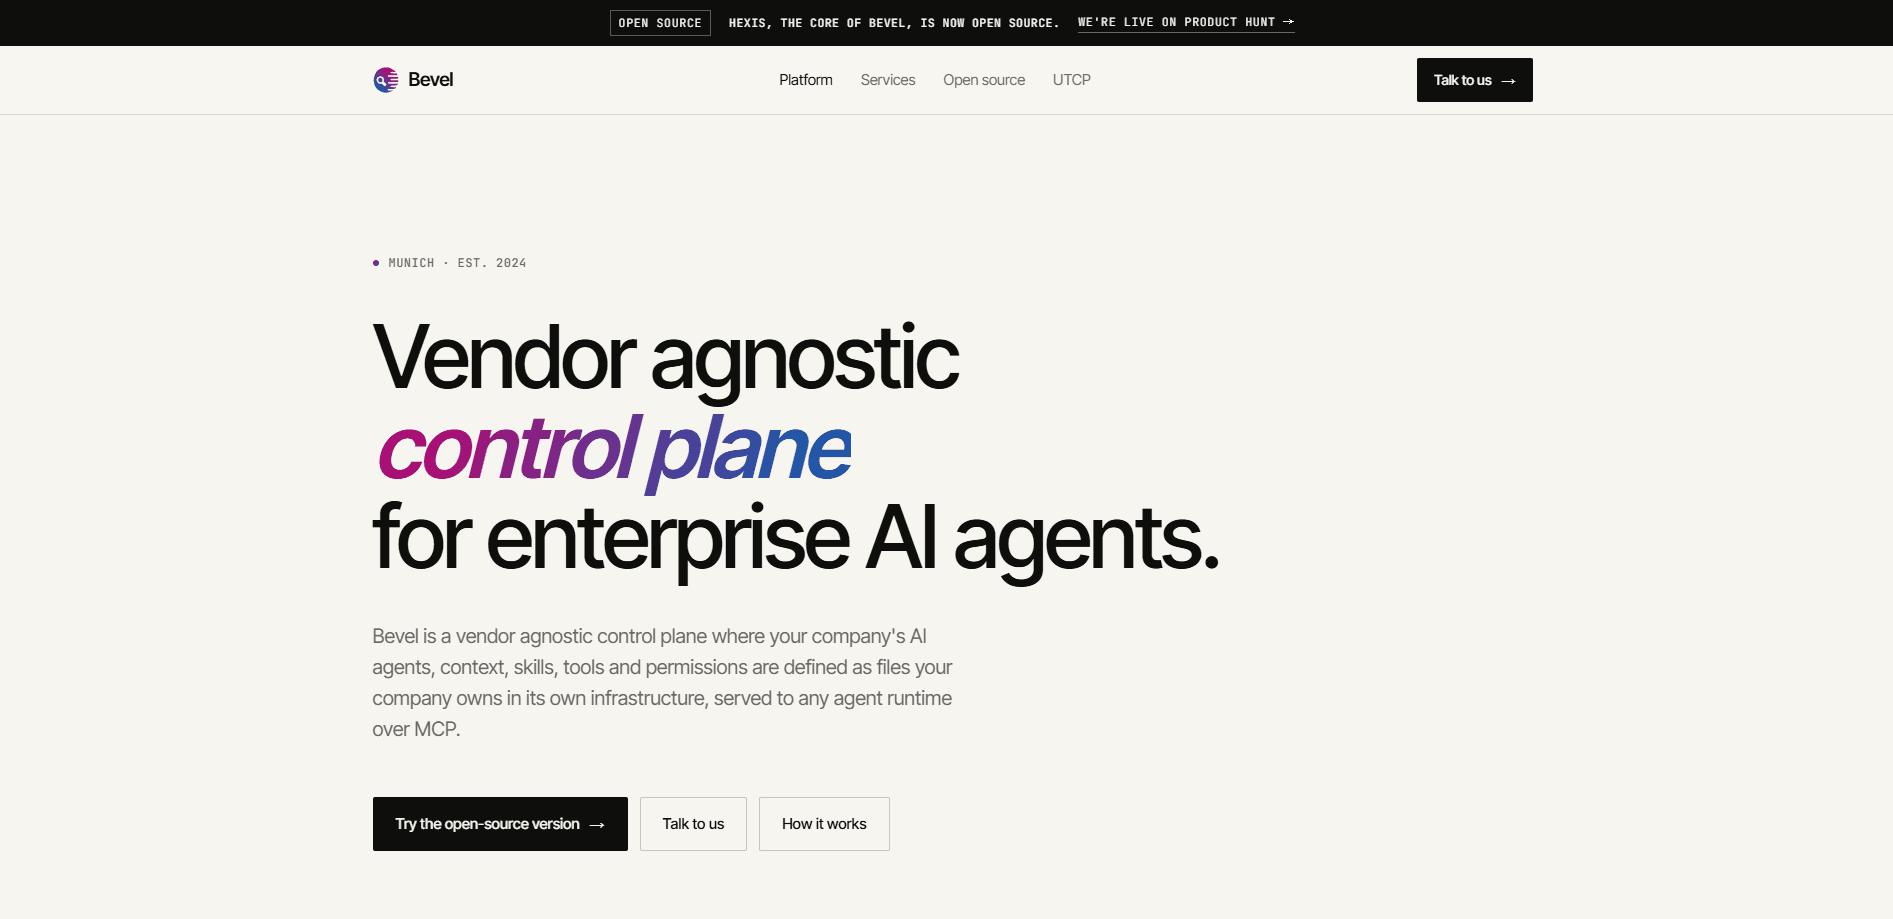
Bevel is a vendor-agnostic control plane for enterprise AI agents, built by a Munich team founded in 2024. It lets a company define its agents, context, skills, tools, permissions, and identity as plain files in its own repository, then serves those files to any agent runtime over MCP or UTCP. The pitch is simple. If your agents live inside someone else's product, you don't really own them. Bevel wants the source of truth to sit in your own infrastructure.
About Bevel
What Is Bevel
Bevel is an infrastructure layer that sits between a company's knowledge and whatever AI runtime its employees happen to use. Instead of scattering instructions in a vendor's config, tool wiring in per-vendor connector panels, and knowledge in per-vendor grounding stores, Bevel keeps all of it as Markdown and YAML files in a Git repository you control.
The product treats four things as the full specification of an agent: what it knows, how it works, what it may do, and who it acts as. Context, skills, tools, permissions, and identity each become an artifact you can diff, review, and version like any other code.
The main limitation is scope. Bevel targets engineering and operations teams at companies already running agents in production, not individuals or small teams looking for a quick chatbot. There's no public pricing, no free tier listed on the site, and setup assumes you're comfortable with Git, YAML, and MCP. If that sounds like a lot, it probably is. For the audience it's built for, that's the point.
Getting Started
- Set up a Git repository to hold your agent files, with separate folders for knowledge, skills, tools, agents, and access policy.
- Write your context as knowledge nodes and your procedures as Markdown skills, so they're readable and reviewable in a diff.
- Declare tool manifests and let Bevel hold secrets in a vault, then write access rules that say which agent may read which file and call which endpoint.
- Define each agent as a named actor with its own credentials and scope, so every action is attributable to it.
- Connect your runtime of choice and let it read exactly what it's permitted to read over MCP or UTCP.
Product Information
A quick look at Bevel's pricing, supported platforms, and performance.
Best for
The users, tasks, and scenarios where this tool fits best.
Users
- Platform and DevOps engineers
- Enterprise IT and security leads
- Teams running agents across multiple vendors
Tasks
- Centralizing agent context
- Governing tool access
- Standardizing skills
Scenarios
- Migrating agents off a vendor's closed platform
- Auditing what an agent did
- Onboarding a new runtime
Key features
Git-backed source of truth
This git-backed agent platform keeps your repository holding the knowledge, skills, tools, agents, and access policy. Branches, change requests, and diffs come from Git rather than a custom review system, which means your existing workflow and tooling carry over. Every edit is versioned and reversible.
Vendor-agnostic control plane
Bevel doesn't lock you to one runtime. It serves the same definitions to Claude Code, Cursor, ChatGPT, opencode, background agents, and self-hosted in-platform agents. Switch tools and nothing breaks. The context and skills you built don't have to be rebuilt.
Context with provenance
Knowledge is stored as typed nodes, and every fact tracks where it came from, who last touched it, and when it was verified. The nodes compile into a graph you can traverse, mass-update, and build dashboards on. Why does that matter? Teams need to answer why an agent believed something. This is the difference between a claim and an audit trail.
Skills as written procedures
Skills aren't prompt fragments buried in a config file. They're procedures written in plain Markdown, readable by the people who own the process and reviewable in a diff. That makes them portable across runtimes. It also makes handoffs easier when staff change.
Tools, permissions, and secrets
Tool manifests declare what an agent can call, while secrets sit in a vault rather than pasted into connector panels. Access rules spell out which agent may read which file and call which endpoint. This is where most of the AI agent governance lives. Changes go through review like everything else, so a single misconfigured permission doesn't slip through unnoticed.
Per-agent identity
Each agent is a named actor with its own credentials and scope, not a shared service account. Not a shared login. Every action is attributable to a specific agent, which matters when you need to trace a bad output back to its source.
Pros and cons
Pros
- Keeps agent definitions in your own repository, so you're not dependent on a vendor's product to preserve them.
- Context, skills, tools, permissions, and identity are handled together instead of across separate per-vendor panels.
- Git-based review, diffing, and rollback come for free because the artifacts are files.
- Per-agent credentials and file-level access rules give security teams something concrete to audit.
- Serves multiple runtimes over MCP and UTCP, which lowers the cost of switching tools.
Cons
- No public pricing or free tier is listed, so budget planning means talking to the vendor first.
- Setup assumes real comfort with Git, YAML, and MCP; there's no drag-and-drop onboarding for non-technical users.
- It's aimed at enterprises, so individuals and small teams are likely to find it heavier than they need.
Frequently asked questions
Bevel is a control plane that defines your AI agents as files in your own Git repository, then serves those definitions to any agent runtime over MCP or UTCP. It covers context, skills, tools, permissions, and identity in one place.
Related content
Explore related tools, skills, and articles for Bevel.
Bevel Alternatives
Forefront
Forefront · CodingForefront is a web platform for building with open-source AI. It lets you fine-tune leading open-source language models on your own data, evaluate how they perform, and run them through an API or export them to host yourself. Developers who want the convenience of a closed-source platform but insist on owning their models and data are the target audience here.

Startkit
StartKit.AI · CodingStartkit is a boilerplate for building AI SaaS and AI wrapper products. Think of it as an AI startup boilerplate with the boring parts already wired up: authentication, Stripe and Lemon Squeezy payments, usage limits, transactional email, and an AI API starter that talks to OpenAI, Anthropic, Groq, or Llama. You clone the repo, set your price, and start on the part of your product that people actually pay for. It's Next.js under React and Tailwind, so most of the boilerplate code already feels familiar.
Testim
Tricentis · CodingTestim is an AI-powered test automation platform for building and running end-to-end tests across web, mobile, and Salesforce applications. It leans on machine learning to keep tests stable when an interface changes, so teams spend less time fixing broken selectors. Not bad for an automated testing tool you can start using today. You create tests by recording actions in a browser, then optionally add JavaScript when you need more control. It's a solid pick for busy QA teams.